
Implementation and certification support
A part-time security officer leads the implementation and prepares your company for the certification audit, without hiring a full-time specialist.
More about the service → NIS2Cybersecurity risk management for essential and important entities
Prepare your company or institution for audit, certification and compliance with ISO 27001, NIS2 and other requirements.
By clicking “Try it free” you accept the Terms of Service and the Privacy Policy.
14 days freeNo payment cardThe trial runs the ISO 27001 path
Our team supports implementation, tests your security and carries out audits.
A part-time security officer leads the implementation and prepares your company for the certification audit, without hiring a full-time specialist.
More about the service →Vulnerability assessments and testing of web applications, APIs and mobile apps, with results ranked by risk.
More about the service →External and internal penetration tests and ISO 27001, NIS2 and DORA audits, with a list of gaps and an action plan.
More about the service →See where your company stands today. You get the result straight away or at your work email address.
Answer questions about your company and see how close you are to certification.
Take the test →Pick a situation and see how Guardiso helps.
You pick the standard and answer questions about your company. Guardiso breaks down the requirements, suggests owners and prepares draft policies for your review.
See what needs action, which risks are open and what is missing before the audit.
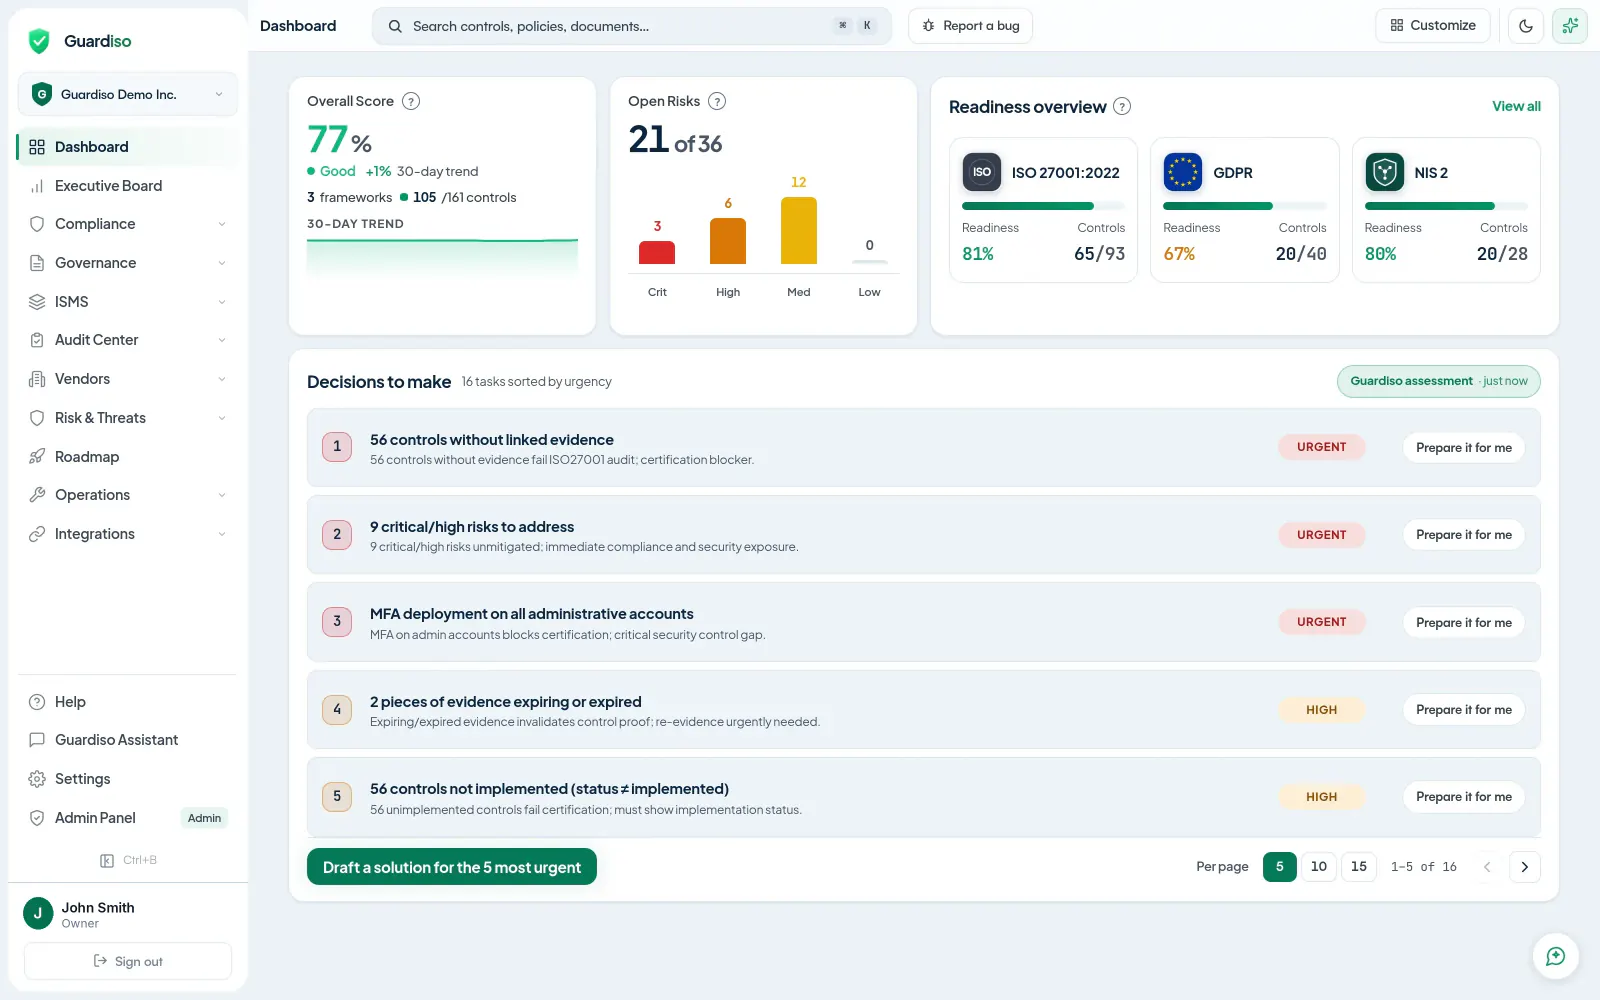
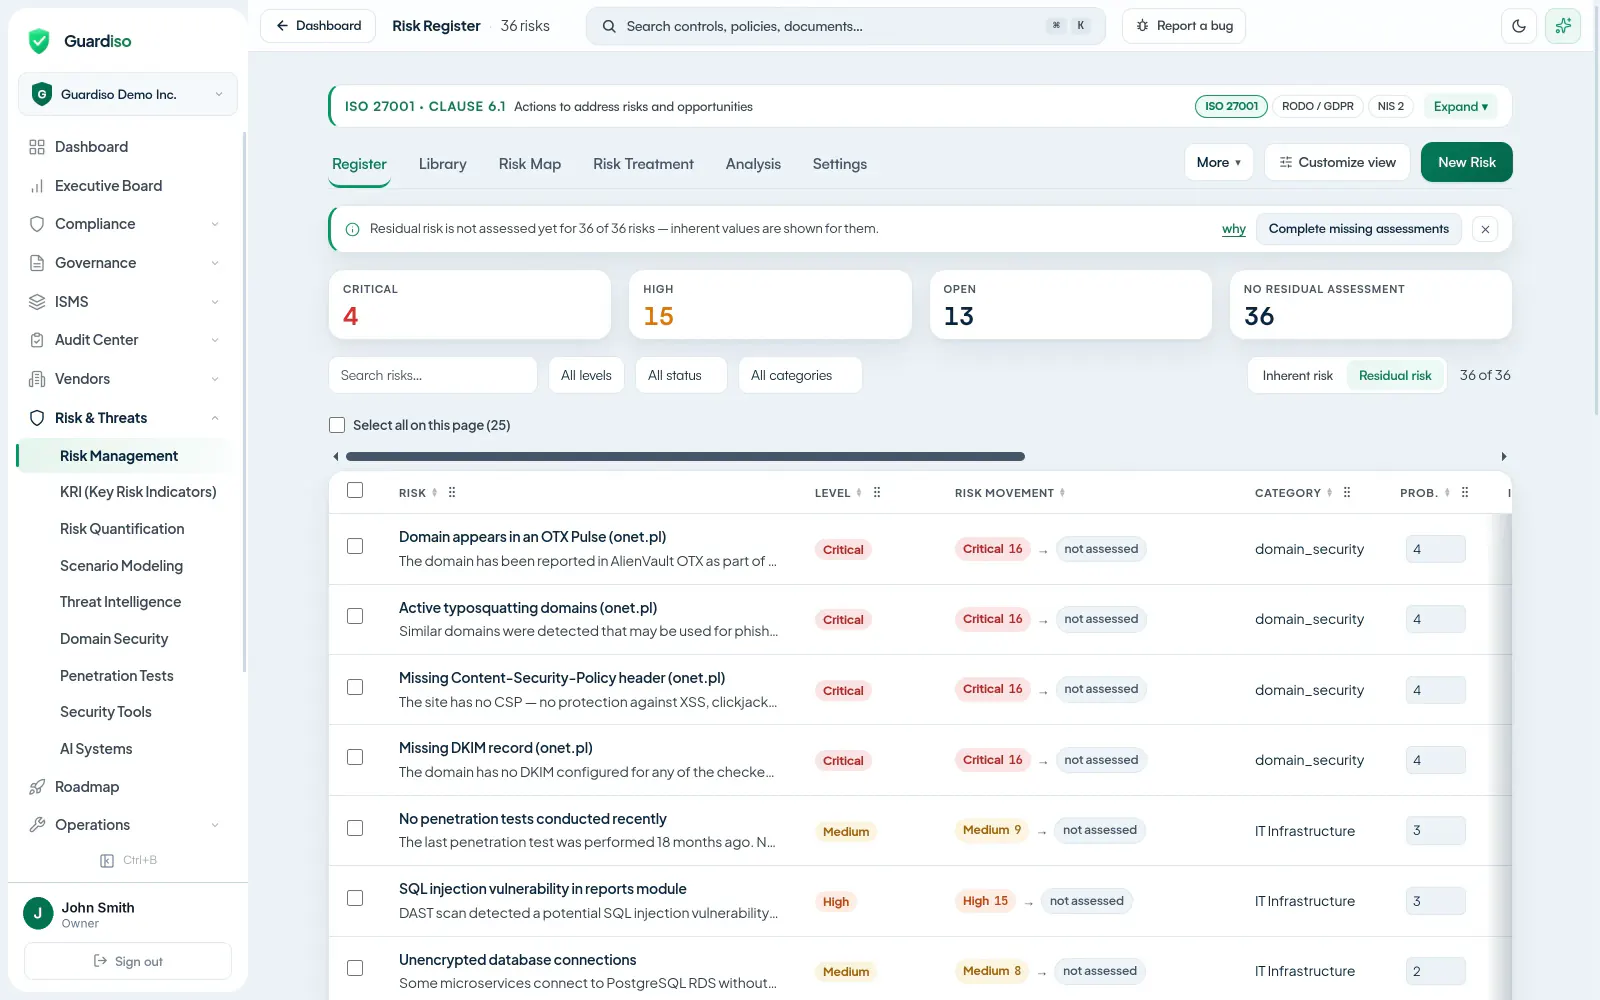
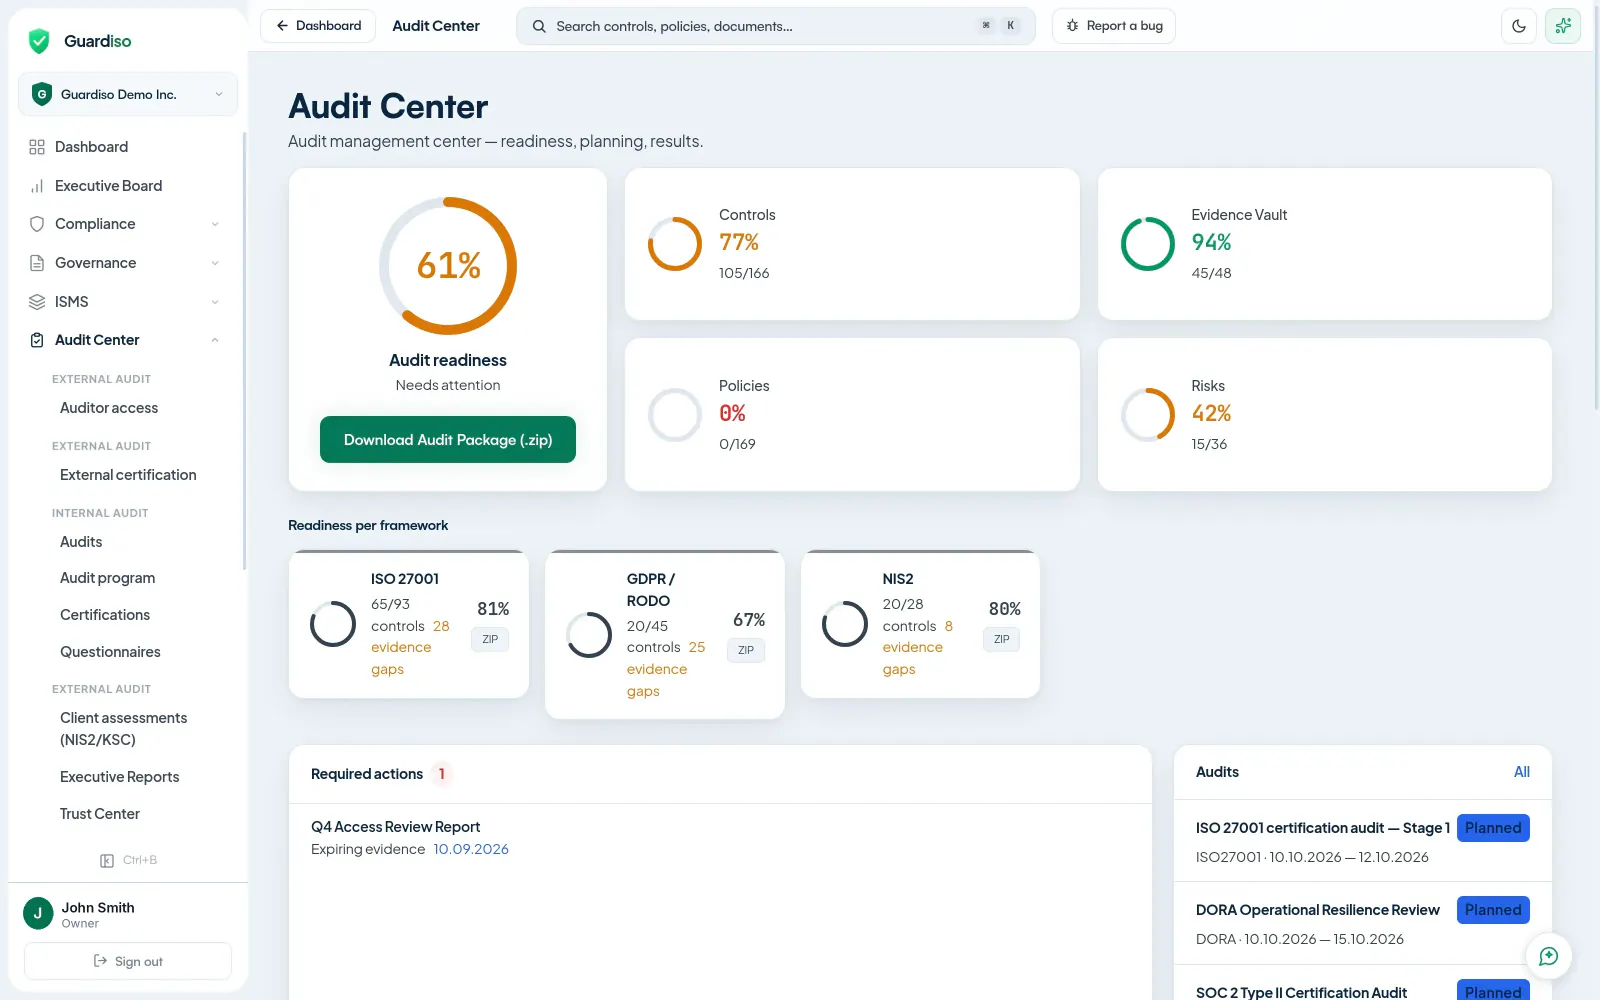
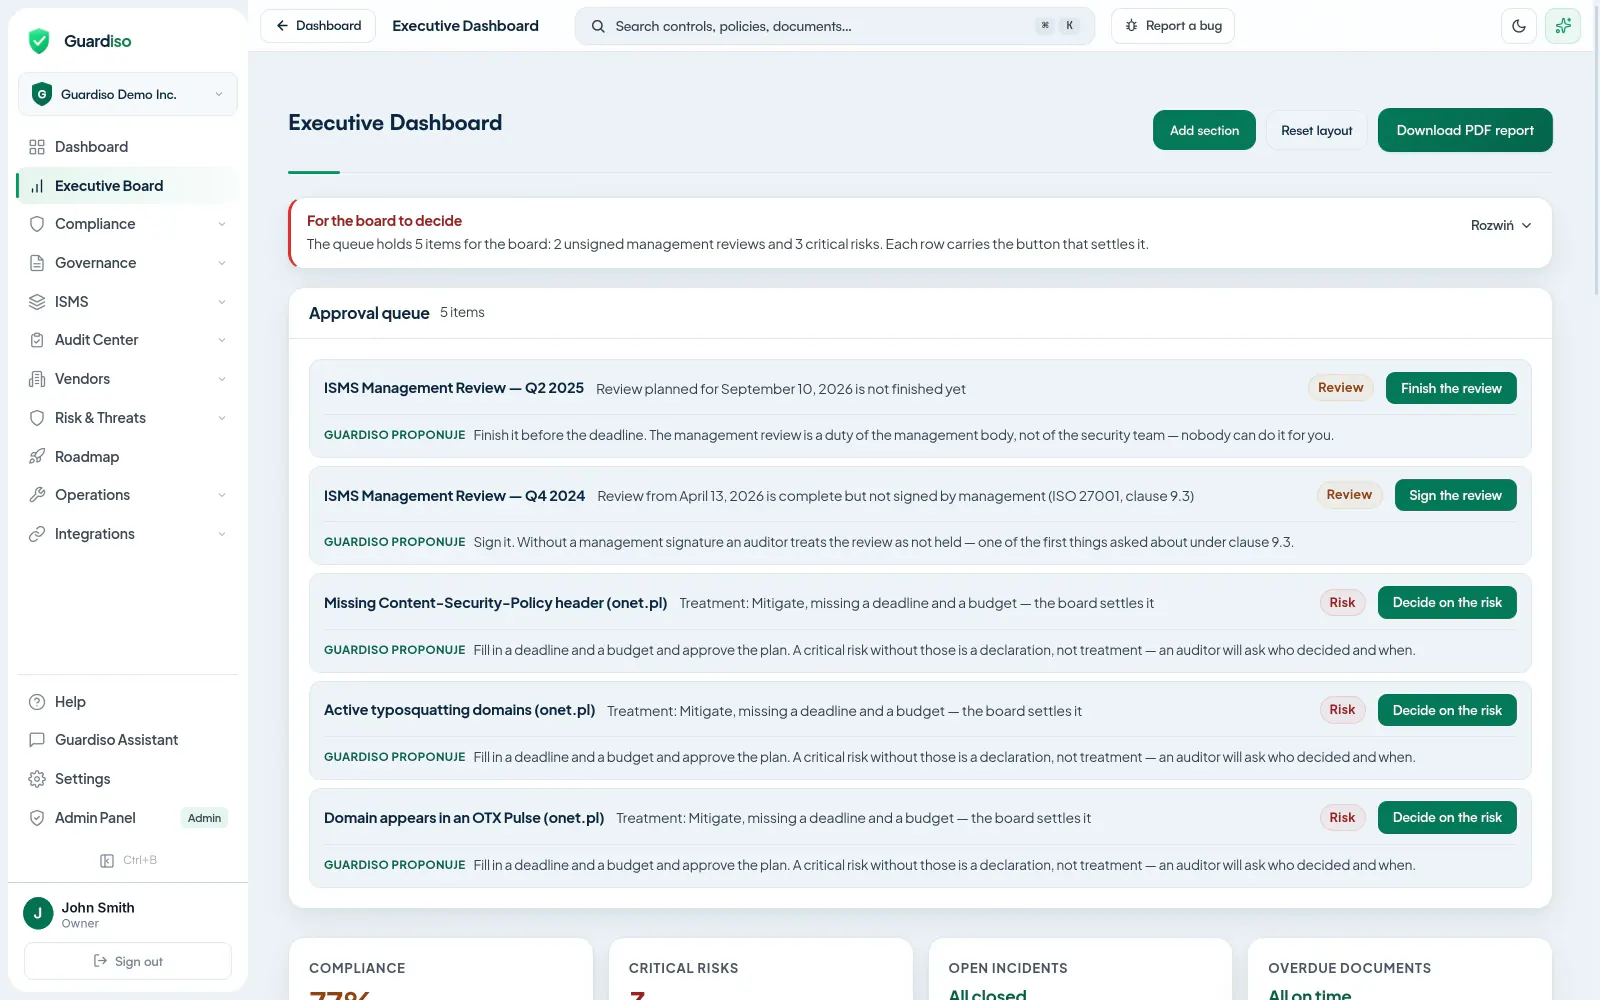
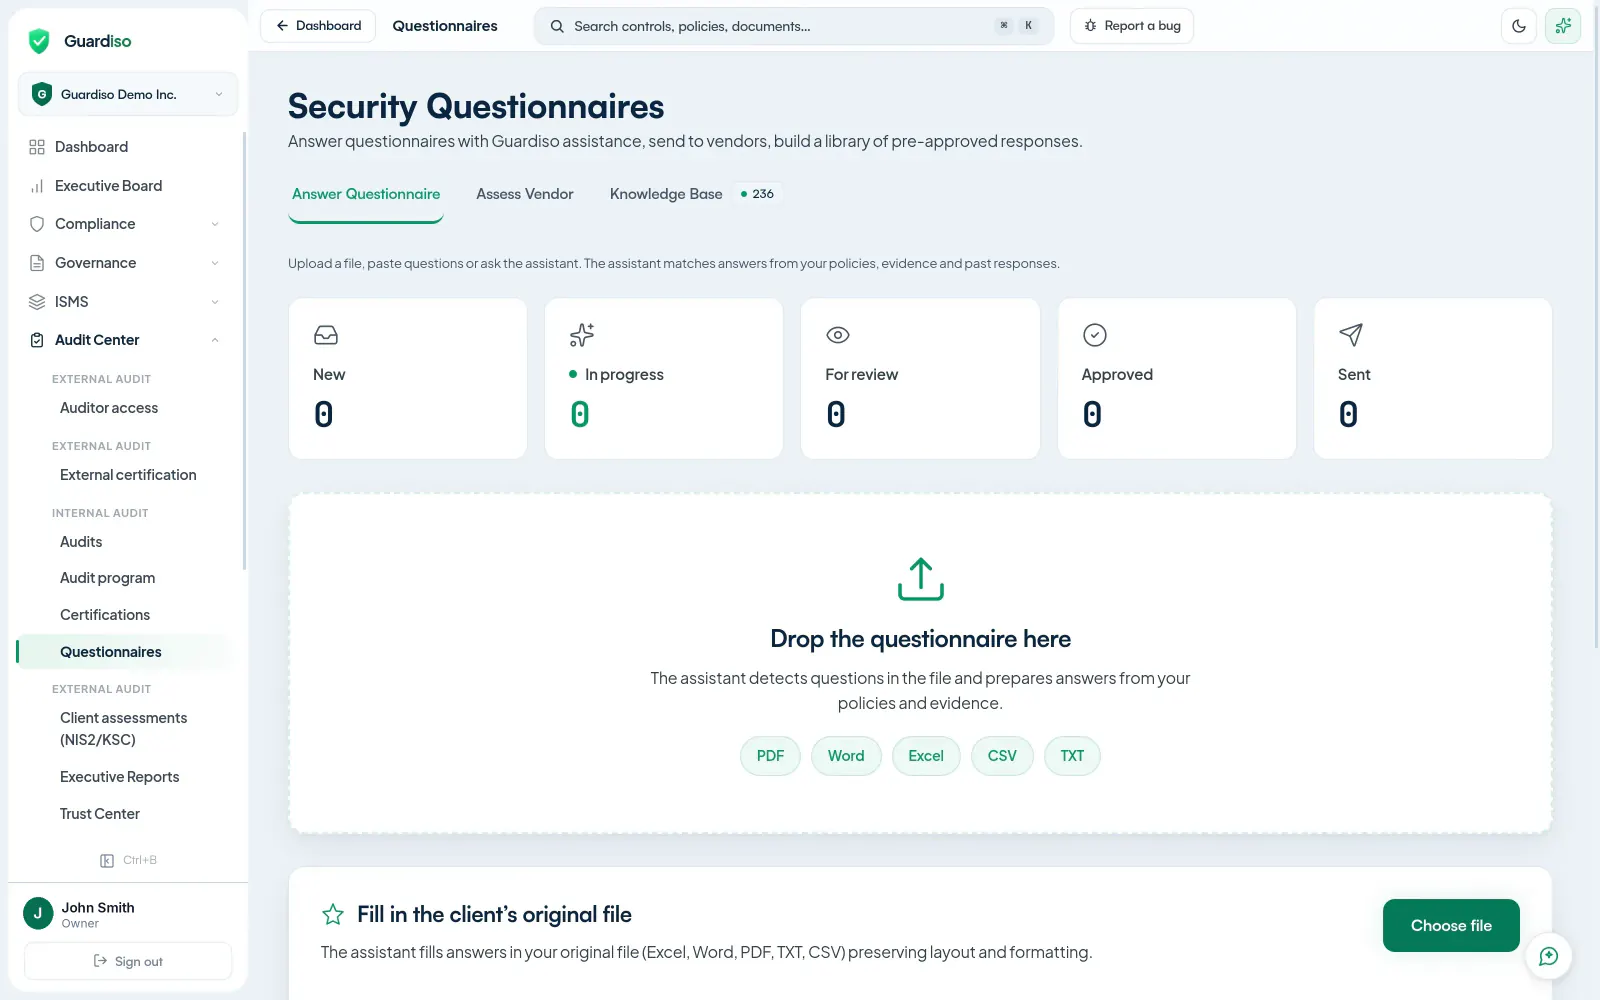
ScreenshotDashboard: You see the most urgent tasks and the next steps.
See how requirements of different standards and regulations connect. You reuse the same documentation and evidence where it applies.
CC3.3 · CC5.2 · CC6.1
Art. 25(2) · Art. 29
Reg. 2024/2690, point 11.1
Art. 9(4)(c)
Guardiso is a GRC platform, for governance, risk and compliance. It runs an information security management system, an ISMS, under NIS2 and ISO 27001. It also covers ISO 9001 and the other rules a company is subject to.
Yes. The platform, database and backups run with a European cloud provider in Poland. E-mail is sent from Ireland and payments are handled by a European entity. When you use the artificial intelligence features, only the query text reaches the model provider; it is not stored there and is not used to train models. The full list of processors is on our subprocessors page.
You sign in with a code sent to your work e-mail address or with a Google account. You connect the systems your company runs on, among them Microsoft 365, Google Workspace, GitHub and Slack. You choose the standards that apply to your organisation. Guardiso starts pulling settings and evidence from those systems, and we guide you through the next steps.
Yes. The requirements are available in Polish, together with ready policy templates and incident handling that keeps track of reporting deadlines. For public entities we also run the annual audit required by the Polish interoperability framework, known as KRI.
Yes. An external auditor gets read-only access through a separate portal, without an account in your organisation. You decide the scope of the material you share. You can see when the auditor was last in the portal, and every action they take is written to the event log.
The artificial intelligence prepares a draft document, points out risks and suggests tasks. Nothing counts as done until you approve it, and every change is recorded in the history together with the person who made it.
Current prices and what each plan includes are on the pricing page. The trial is free and you decide afterwards whether to stay. See pricing →
No. You sign up with your work e-mail and use the platform for 14 days without entering a card. The trial ends on its own and never turns into a paid plan without your decision.
No, and we do not promise that. Guardiso organises the work, keeps the documentation and prepares the organisation for an audit, but a certificate is always granted by an independent certification body after its own examination. The platform makes sure you walk into that examination prepared.
Start a free trial and see how you work with requirements, documentation and tasks.
By clicking “Try it free” you accept the Terms of Service and the Privacy Policy.